Finding a possible flaw in code and showing how it can be exploited are different steps. That distinction helps explain the number OpenAI reported on November 4, 2026. In a research run conducted in mid-October, the team says it reproduced 1,724 vulnerabilities and produced 948 working local privilege escalation exploits for a commonly used Linux distribution in a controlled environment. OpenAI’s technical report
What is local privilege escalation?
An ordinary Linux account has limited permissions. The root account can perform administrative operations, such as modifying system files that ordinary users cannot change.
A local privilege escalation vulnerability can let someone who already has the ability to run code on a machine gain permissions they didn’t start with. Imagine a program running under an ordinary account. If exploiting a kernel flaw gives that program root privileges, it has crossed the boundary between ordinary and administrative access. That’s the kind of outcome the researchers tested for. Scope of the OpenAI study
How did the AI verify the flaws?
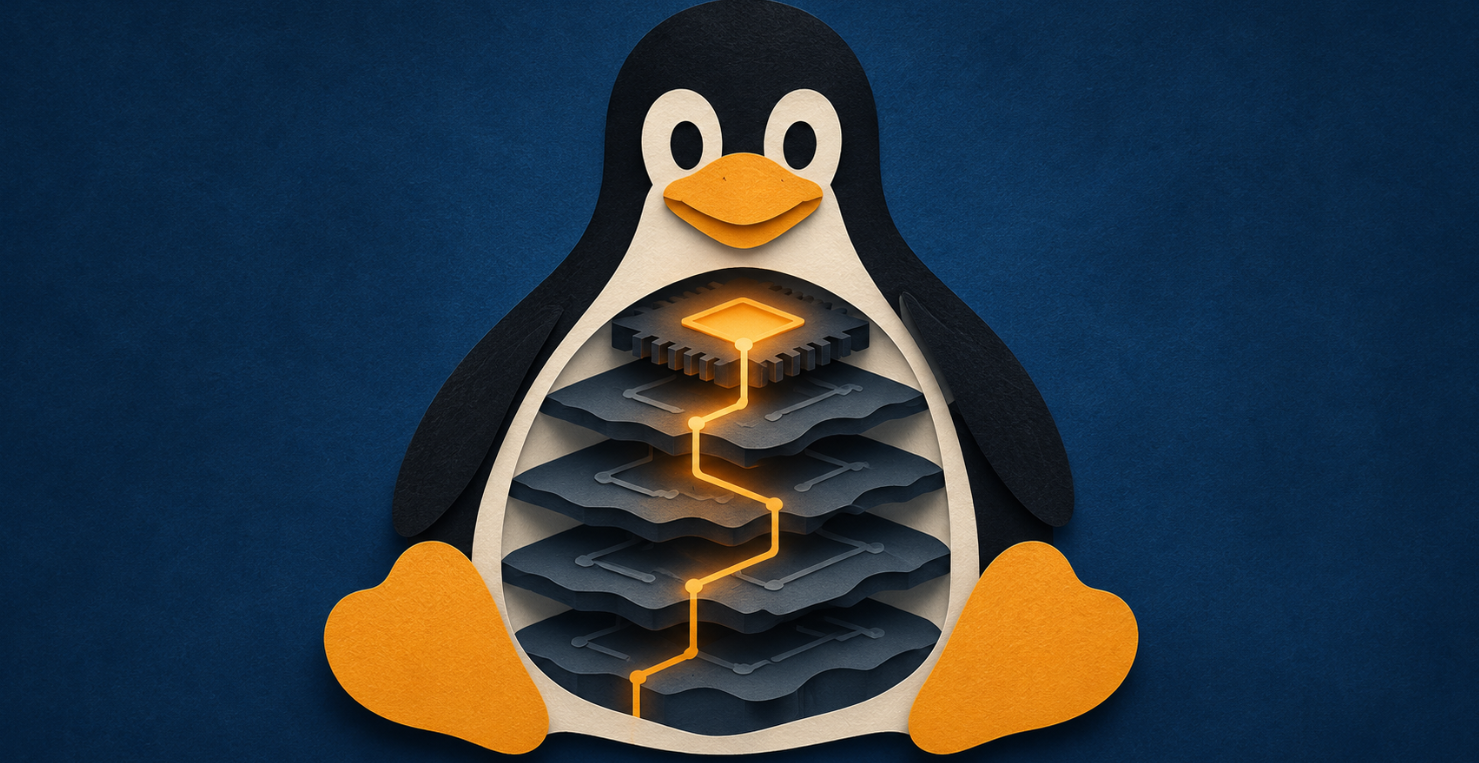
The system examined parts of the Linux kernel for potential security issues, then tried to reproduce the findings in an isolated environment. It generated proof-of-concept exploits to demonstrate what the flaws could do and prepared candidate patches. Human security researchers reviewed the results before reporting the findings. OpenAI’s research method
Each stage answers a different question:
- Potential flaw: Is there something in the code worth investigating?
- Reproduced vulnerability: Can the team trigger the problem in a test?
- Working exploit: Can the flaw be used to achieve a specific outcome, such as gaining root privileges?
- Candidate patch: Is there a proposed code change that maintainers can review and test?
What should Linux users take from the result?
If you’re checking whether a particular system is affected, start with your Linux distribution’s security advisories and the version of the kernel you’re running. The research report describes what the team demonstrated. Distribution advisories are where users can check which versions are affected and which fixes are available.
The 948 working exploits show the scale at which the research system could validate a specific class of Linux flaws under test conditions. For users, the next milestones are maintainers reviewing the proposed changes and distributions shipping the fixes they adopt. OpenAI’s findings
For more on recent AI model releases and availability, see Enzvia’s AI Model Release Tracker.